KnowYourRisk.
A multidisciplinary cybersecurity collective. Red team and blue team, GRC and engineering - different expertise working as one to find the risk before it finds you.
You do not need a security background to read this site. Pick a path.
Recognized by the Bodies That Set the Standard
Founder Nwachukwu Francis O. and penetration tester Ridwan Adebayo hold individual membership with the Cyber Security Experts Association of Nigeria, the national umbrella body for cybersecurity professionals. CYPHRA LTD is registered with the Corporate Affairs Commission, Nigeria under RC 9910674, and is also recognized by NGX Regulation Limited to conduct vulnerability assessment and penetration testing exercises on the online trading portals of Trading License Holders in the Nigerian capital market.
Credentials Across the Disciplines
Our team holds current certifications across offensive security, application security, cloud, and blue team operations.
Penetration Testing
CPTS
Hack The Box
Professional Pentesting
eCPPT
INE Security
Web App Pentesting
eWPT
INE Security
Application Security
CAP
The SecOps Group
Network Security
CNSP
The SecOps Group
Cybersecurity
CC
ISC2
Cybersecurity
Professional Certificate
Associate Cloud Engineer
ACE
Google Cloud
Network Defense
Network Defense
Cisco Networking Academy
API Security
ACP
APIsec University
API Security Analysis
CASA
APIsec University
Cloud Engineering (Batch)
ACE
Google Cloud
A Collective Built on Proof, Not Promises
Different disciplines. One standard. Measured entirely on the risk we reduce and the resilience we build.
$0+
Bounty Earnings
0
Accepted Disclosures
9.1
Highest CVSS Score
P2
Tesla Severity
Red Team. Blue Team. GRC.
We combine offensive and defensive security perspectives with governance, risk, and compliance - a super team of cybersecurity.
We attack like an adversary would, before they do. Authorized, documented, and built to hold up under scrutiny.
Our offensive team simulates real world attackers against your systems. From recon to exploitation, every engagement identifies the vulnerabilities that actually matter and validates them end to end.
Penetration Testing & VAPT
Network, web, mobile, API, and cloud penetration testing
Red Team Operations
Full scope, multiple vector simulated attacks
Web & API Security
Application assessment driven by business logic
Cloud Security Review
AWS, GCP, and Azure misconfiguration hunting
Wireless & Network Testing
Infrastructure compromise, internal and external
Local Business on a Global Collective
Delivered across multiple locations through a globally connected team - consistent standards, reliable communication, and effective delivery regardless of region.
Proven Against Real Targets
Real reports, accepted and paid by the programs. Scroll on for the full stories, explained in plain language.
Read the full stories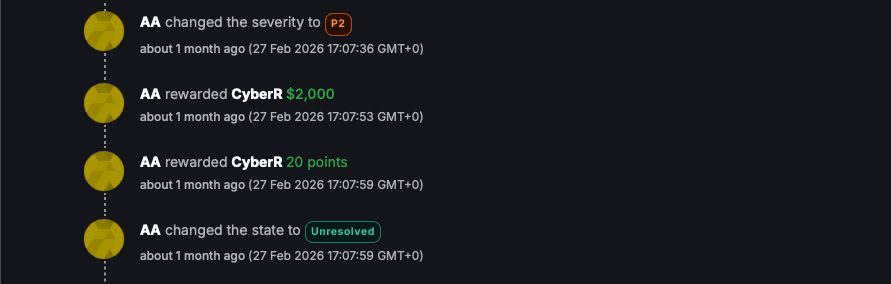
Tesla
Ridwan Adebayo (CyberR) · Bug bounty program
Real findings. Real bounties. Every file in the stack is a disclosed report by our researchers, paid and closed by the program.
Wildcard queries on a partner portal exposed the internal employee directory, including personal mobile numbers, reporting lines, office locations, and internal group memberships. Two companion flaws leaked developer emails with full schema docs plus global ticket counts. Triaged as P2 and paid $2,000.
Ridwan Adebayo (CyberR)
Tesla
An auto confirmed signup flaw issued valid sessions without inbox access, and client controlled metadata led straight to admin. Scored CVSS 9.1 and paid $1,800 after successful reproduction.
Ridwan Adebayo (CyberR)
Enterprise SaaS
An exposed frontend config leaked API secrets plus a login ID with zero authorization checks, so any LINE account holder got a valid token. One unguarded microservice allowed data injection, and the same flaw lived in INT, PRP, and PRD, earning a payout per environment.
Ridwan Adebayo (CyberR)
Luxury Brand
Replaying a settled checkout minted fresh compute credits without fresh payment. The missing idempotency check turned one purchase into endless machines, filed as a public advisory with video proof and formal credit.
Abang Obed (d3vobed)
CodeSandbox
A file that is a valid archive and valid markup at once slips past upload checks as one thing and executes as the other. Built the payload generator plus minimal servers to reproduce it end to end, assessed P3 S3 with security review engaged.
Abang Obed
Major Browser Vendor
A protected account that cannot be messaged directly still received messages through the mobile post sharing flow. Mapped the exact path with screenshots while the web flow stayed locked, and watched the behavior get fixed.
Abang Obed (obx)
Global Social Platform
We Let the Work Speak for Itself
Six files. Each one starts with a plain explanation of what went wrong, then the technical detail underneath.
Case 01Tesla OData Wildcards to Employee Directory
In plain terms: A search feature on a supplier portal let an outsider page through Tesla's internal staff directory, phone numbers and all.
See case study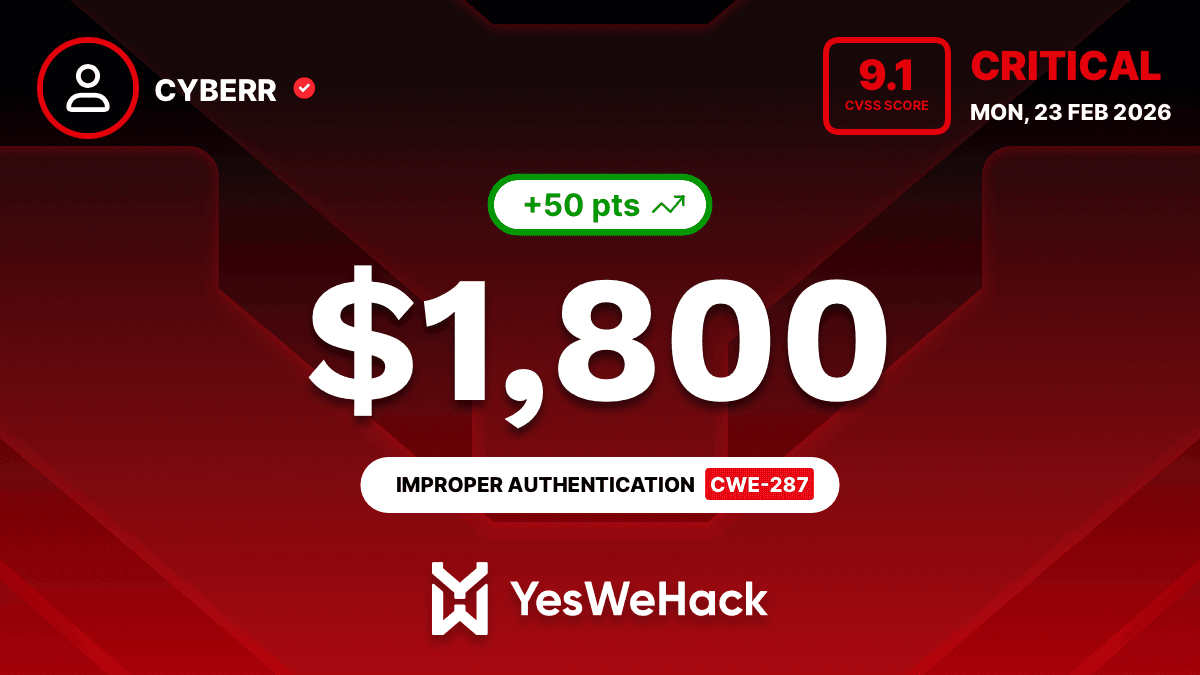 Case 02
Supabase Auth Bypass to Admin
In plain terms: Signing up with a partner email was enough to get a working session, and one form field let anyone claim to be an admin.
See case study Case 03
Luxury SSO Chain to Broken Access
In plain terms: A public settings file handed over the keys, and the login flow never checked who was actually signing in.
See case study Case 04
Payment Replay to Free Compute
In plain terms: Replaying an old payment created new credits, like a receipt that works every time you show it.
See case study Case 05
Polyglot Upload to Stored Scripts
In plain terms: One file could pass as a harmless archive and still run code when the browser opened it.
See case study Case 06
Share Flow Restriction Bypass
In plain terms: A private account blocked direct messages, but sharing a post quietly delivered one anyway.
See case studyThat is the proof. Here is the rest.
You have seen the work. Next, see how we approach an engagement, or start a conversation about your own systems.
The Hacking Process, Done Properly
We map your attack surface: domains, infrastructure, applications, cloud, and exposed services, and understand your business objectives.
With Expertise Across the Entire Security Stack
A super team of cybersecurity - offense, defense, governance, and engineering aligned precisely with your business objectives.
 01
We Identify Hidden Vulnerabilities
Manual, adversarial testing that finds what scanners miss: logic flaws, misconfigurations, and exploitable chains.
 02
We Reduce Attack Surface
Prioritized remediation that closes the real paths attackers take, not a generic checklist.
 03
A Team That Works Like a Partner
Offensive, defensive, GRC, network, and software disciplines working as one collective on your bench.
 04
Your Security Is Our Only Metric
We measure success by risk reduced and resilience built, not hours billed or pages delivered.
 05
Long Term Security Maturity
Programs designed for where your business is three years from now, not a three month engagement.
 06
Continuous Optimization
Monitoring, retesting, and tuning between engagements. Security is a process, not a project.
Built on Trust. Driven by Expertise.
CYPHRA - from cipher, the craft of keeping what matters private, intact, and trusted. And like the color purple - blue (defense) meeting red (offense) - we bring different disciplines together into one collective. The team below is that collective.
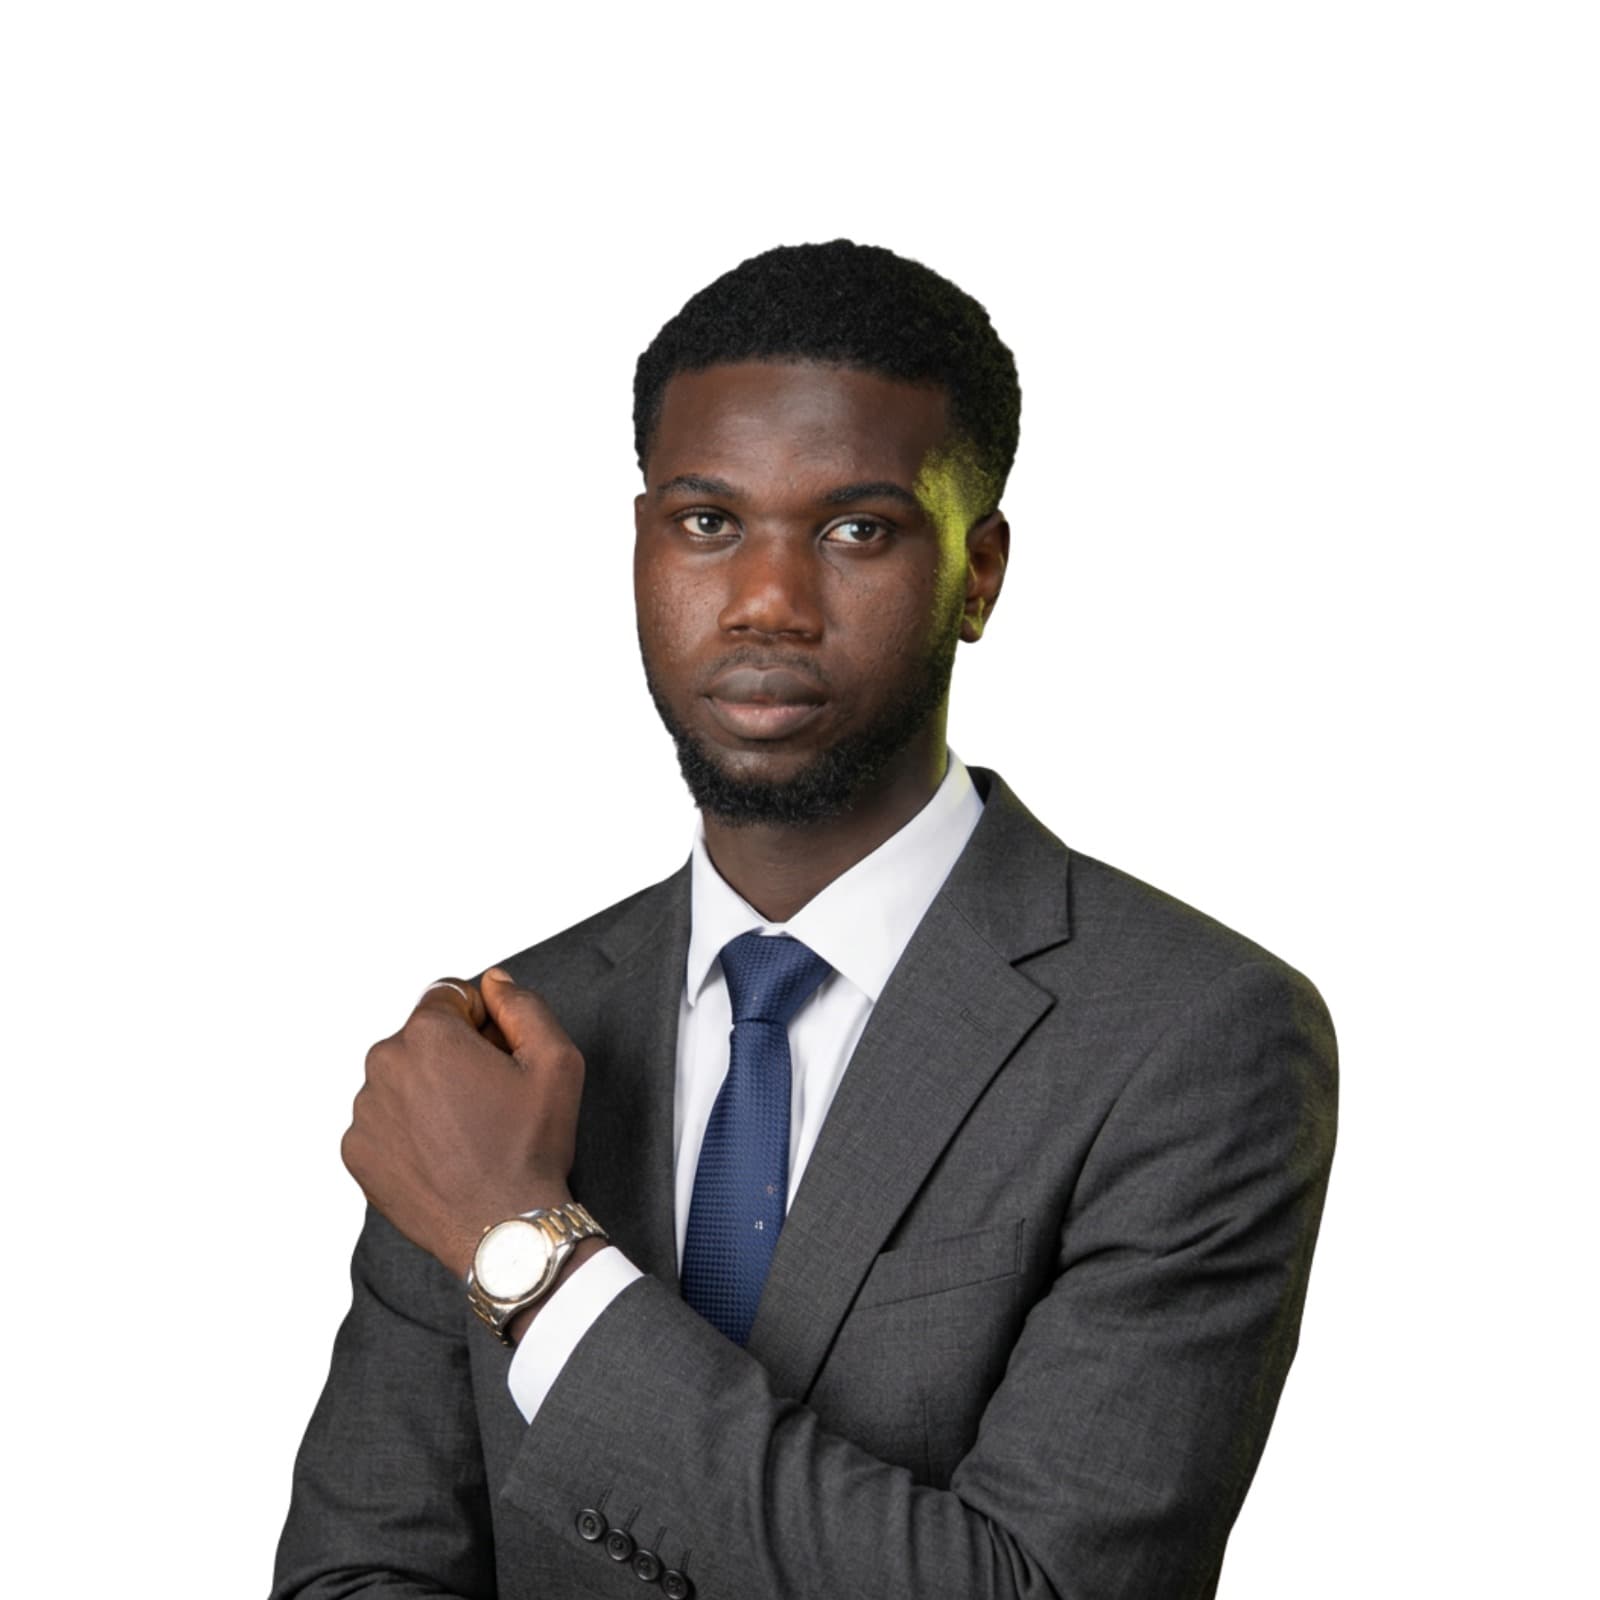
Nwachukwu Francis O.
Founder/Tech Lead
Nwachukwu Francis O.
Cybersecurity analyst working across network security, threat analysis, and SOC operations. Leads CYPHRA's technical bench and brand. Individual member of the Cyber Security Experts Association of Nigeria (CSEAN).
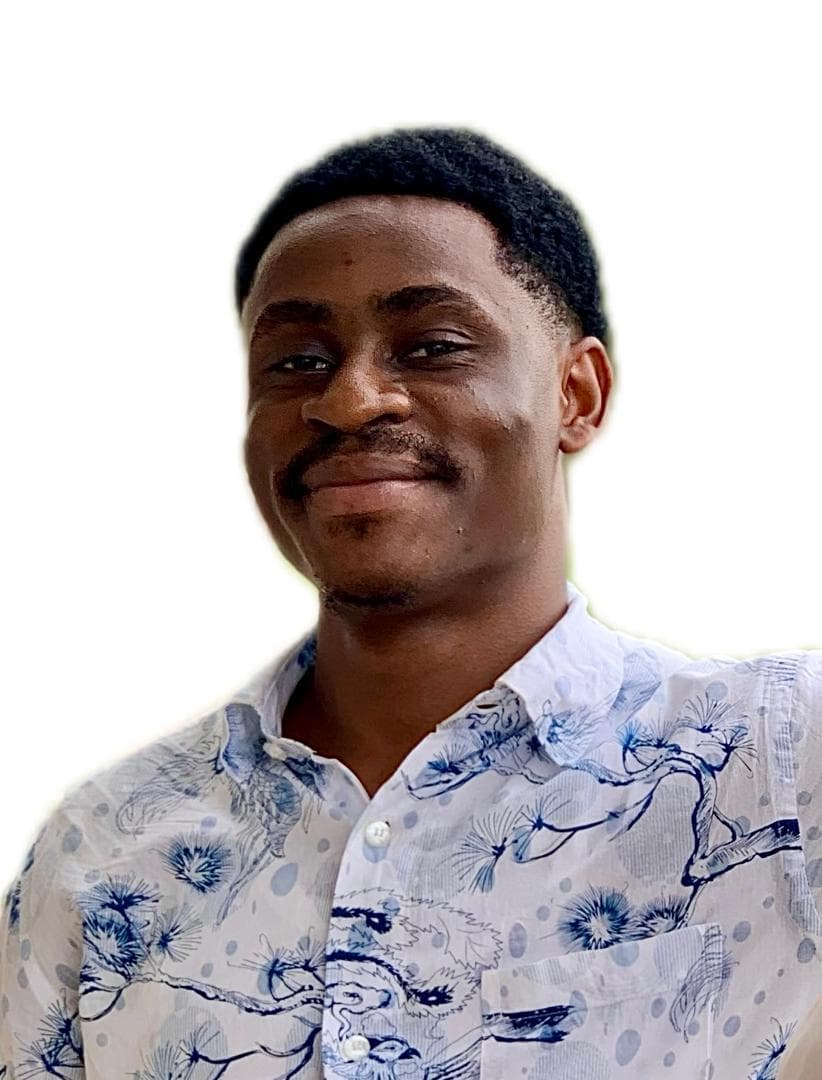
Abang Obed
Offensive Security & Red Team Operations
Abang Obed
Six years across security operations, application security, offensive security, and detection engineering. CPTS certified, credited on GitHub and X security advisories.
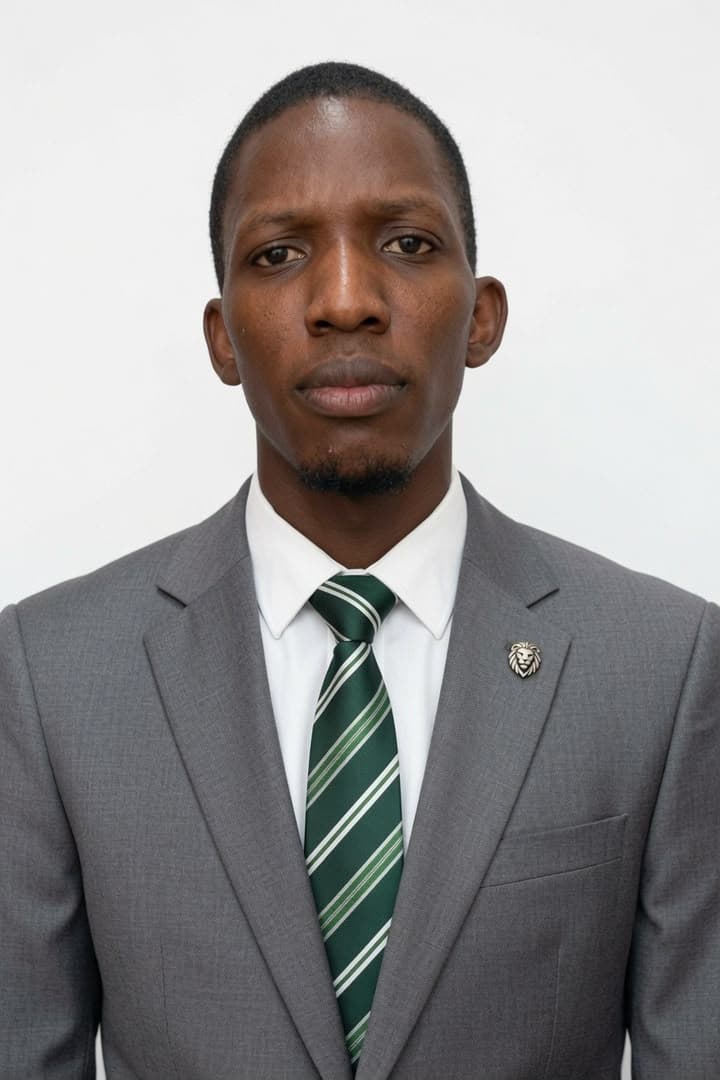
Ridwan Adebayo
Penetration Tester & Cloud Engineer
Ridwan Adebayo
Five+ years in offensive security. Advises Nigeria's Police Force National Cyber Crime Center, 35+ accepted bug bounty reports across Bugcrowd and YesWeHack. Individual member of the Cyber Security Experts Association of Nigeria (CSEAN).
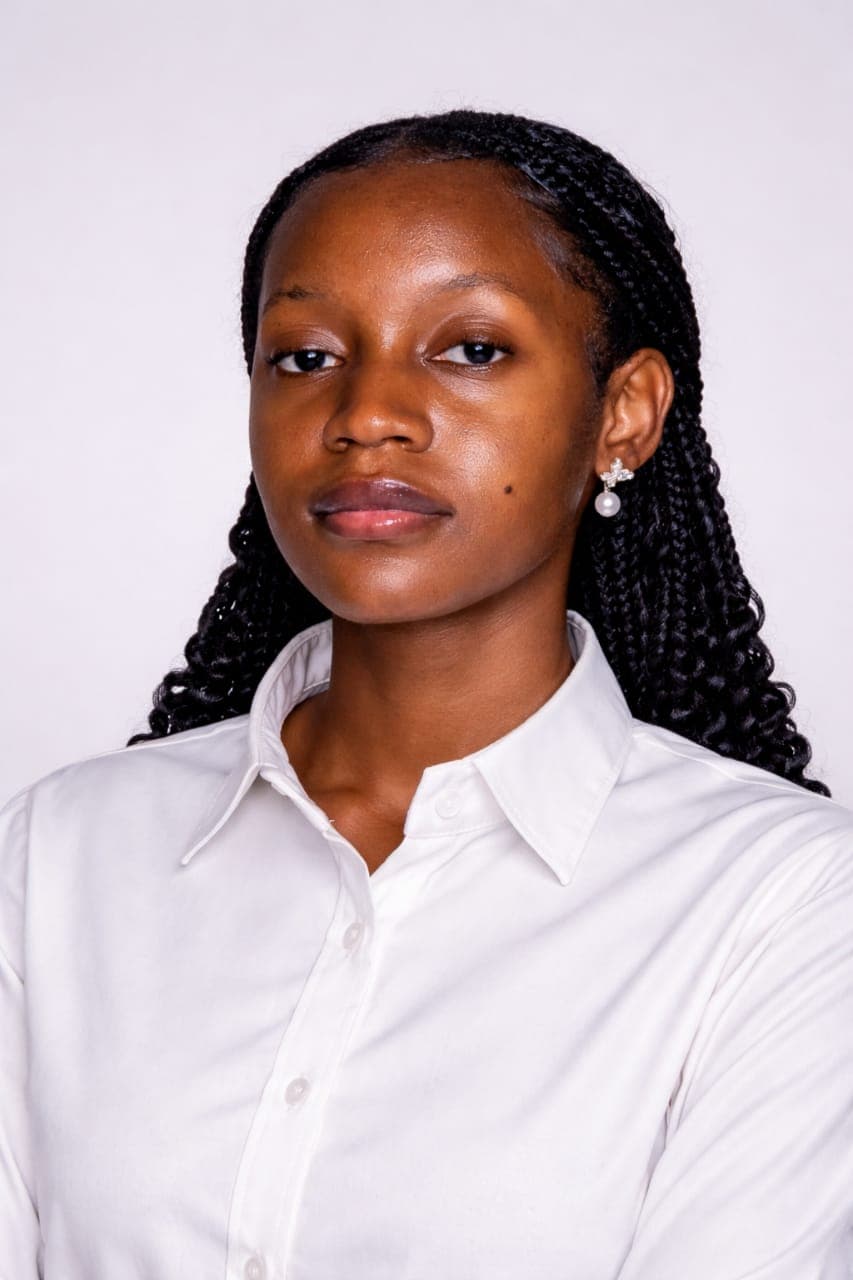
Agnes Akpa
DevSecOps & GRC
Agnes Akpa
Head of Security at FiatRouter. Blends technical depth with risk governance and business alignment. (ISC)2 Certified in Cybersecurity, DevSecOps, and Google Cybersecurity certified.
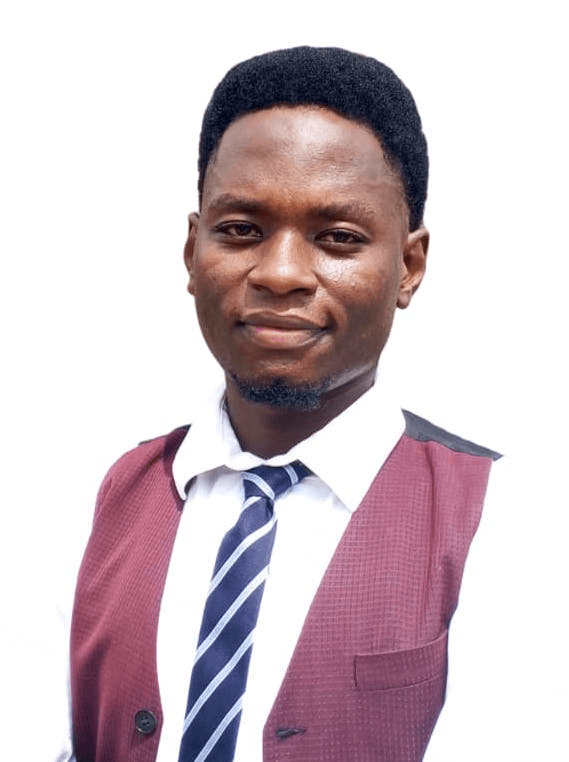
Isah Dauda
Full Stack Developer & Security Researcher
Isah Dauda
Full stack blockchain engineer who audits from the inside out. CAP and CNSP certified, hunts on Cantina, YesWeHack, and Bugcrowd, including XRP Ledger audit contests.
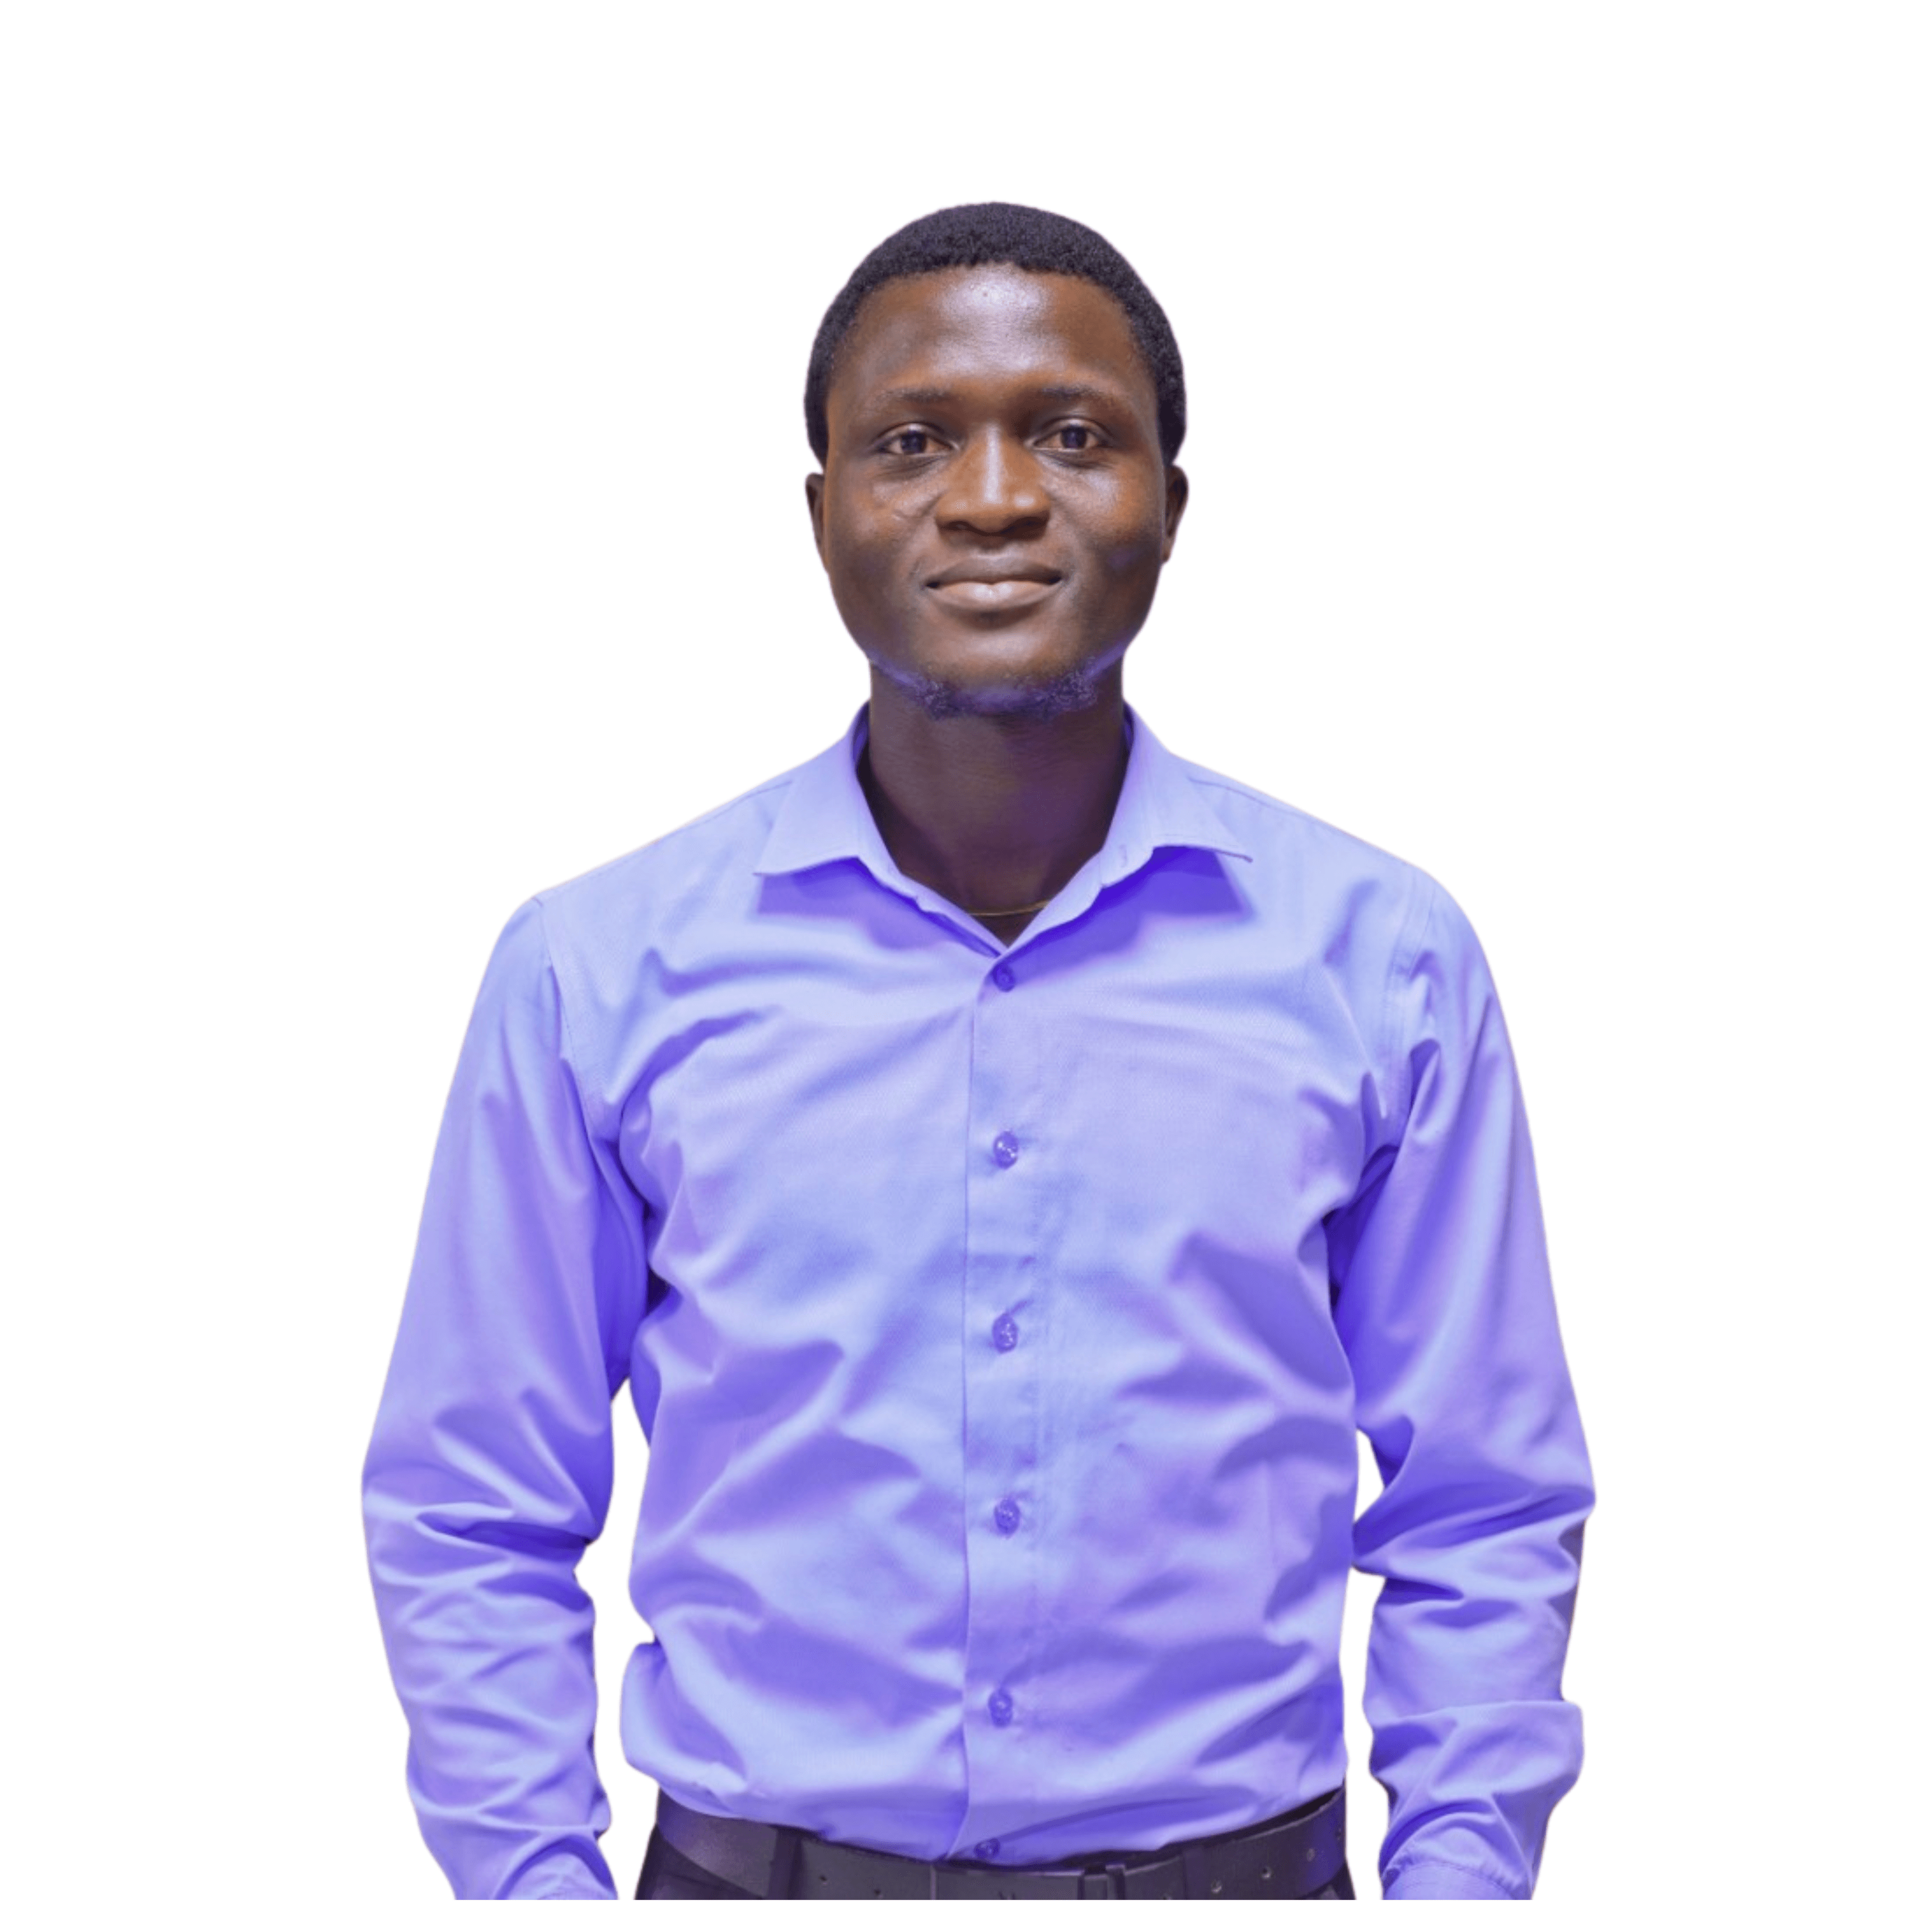
Badu Zaccheaus J.
Cyber Security Analyst & Blue Team Operations
Badu Zaccheaus J.
Hands on testing of production systems: misconfigurations, insecure headers, and web application flaws turned into clear, actionable reports. Part of the discipline behind CYPHRA's methodology: authorized, documented, and built to hold up under scrutiny.
We Know What Different Businesses Need
Whatever stage you are at, if security is the goal, we have done this before.
Startups and Founders
You are building from scratch and every dollar needs to work. We help early stage companies build a secure foundation and attract their first enterprise contracts.
Growing Businesses
You have product market fit and want security that scales. We come in as a strategic partner building detection, testing, and compliance programs that compound over time.
Enterprise & Institutions
You operate at scale across markets and stakeholders. We handle assessments across multiple countries, enterprise GRC programs, and SOC operations where stakes are high.
NGOs & Public Sector
Your audience is donors, constituents, and communities. We deliver compliance aware, budget efficient security that balances reach and credibility.
Your Security Partner, Not Just Another Firm
A super team of cybersecurity, one collective. Let us find the risk before the attacker does.